01
소프트웨어 공급망 보안
Software Supply Chain Security
오픈소스 생태계와 빌드 파이프라인, 서드파티 소프트웨어 생명주기 전반의 의존성을 식별하고 CISA·NIST 표준 기반의 공급망 무결성을 실증 검증합니다.
Hannam University · Software Supply Chain Security
From open-source component analysis and build pipeline integrity verification to runtime remote attestation — identifying supply chain attack surfaces and validating robust defensive mechanisms across modern computing systems.
Who we are
The High Performance & Secure Computing Lab (HPSC) identifies software supply chain attack surfaces throughout the software development life cycle (SDLC) and empirically validates system integrity across computing tiers.
We focus on evaluating the fidelity of CycloneDX and SPDX SBOM generation tools, verifying SLSA-compliant build pipeline integrity, modeling supply chain threats for nuclear I&C and cyber-physical systems, and leveraging hardware-rooted Trusted Execution Environments (TEEs) based on Intel SGX and ARM TrustZone.
Our people →Core Research Domain
Advancing Software Supply Chain Security — focusing on dependency identification, build pipeline integrity verification, and hardware-rooted system security.
소프트웨어 공급망 보안
오픈소스 생태계와 빌드 파이프라인, 서드파티 소프트웨어 생명주기 전반의 의존성을 식별하고 CISA·NIST 표준 기반의 공급망 무결성을 실증 검증합니다.
SBOM 및 무결성 검증 체계
CycloneDX·SPDX 표준 기반 SBOM 생성 도구 신뢰성 평가, 런타임/빌드 타임 SBOM 비교 분석, SaaSBOM 및 AI-SBOM 컴플라이언스 체계를 연구합니다.
핵심 인프라 및 OT 공급망 보안
원자력 계측제어(I&C) 및 국가 핵심 기반시설 제어시스템의 공급망 위협 모델링과 IEC 62443 등 국제 보안 표준 준수 기술을 연구합니다.
신뢰 실행 환경 (TEE 보안)
Intel SGX와 ARM TrustZone 등 하드웨어 격리 기반의 신뢰 실행 환경(TEE) 구축 및 원격 증명(Remote Attestation)을 통한 런타임 무결성을 보장합니다.
바이너리 분석 및 취약점 진단
임베디드 펌웨어 및 다중 아키텍처(ARM/x86) 바이너리를 대상으로 정적·동적 리버스 엔지니어링을 수행하여 공급망 백도어와 취약점을 탐지합니다.
빌드 파이프라인 무결성 및 출처 검증
SLSA 프레임워크 및 in-toto 기반 빌드 파이프라인 무결성 검증, 암호학적 출처(Provenance) 서명 및 증명을 통해 CI/CD 공급망 위협을 원천 차단합니다.
Selected work
Sharing peer-reviewed research across SBOM standards, supply chain threat modeling, and trusted execution environments.
Domestic · Journal
이준희, 정윤정, 이만희
Domestic · Journal
정윤정, 이만희
Domestic · Journal
정윤정, 이만희
Lab notes
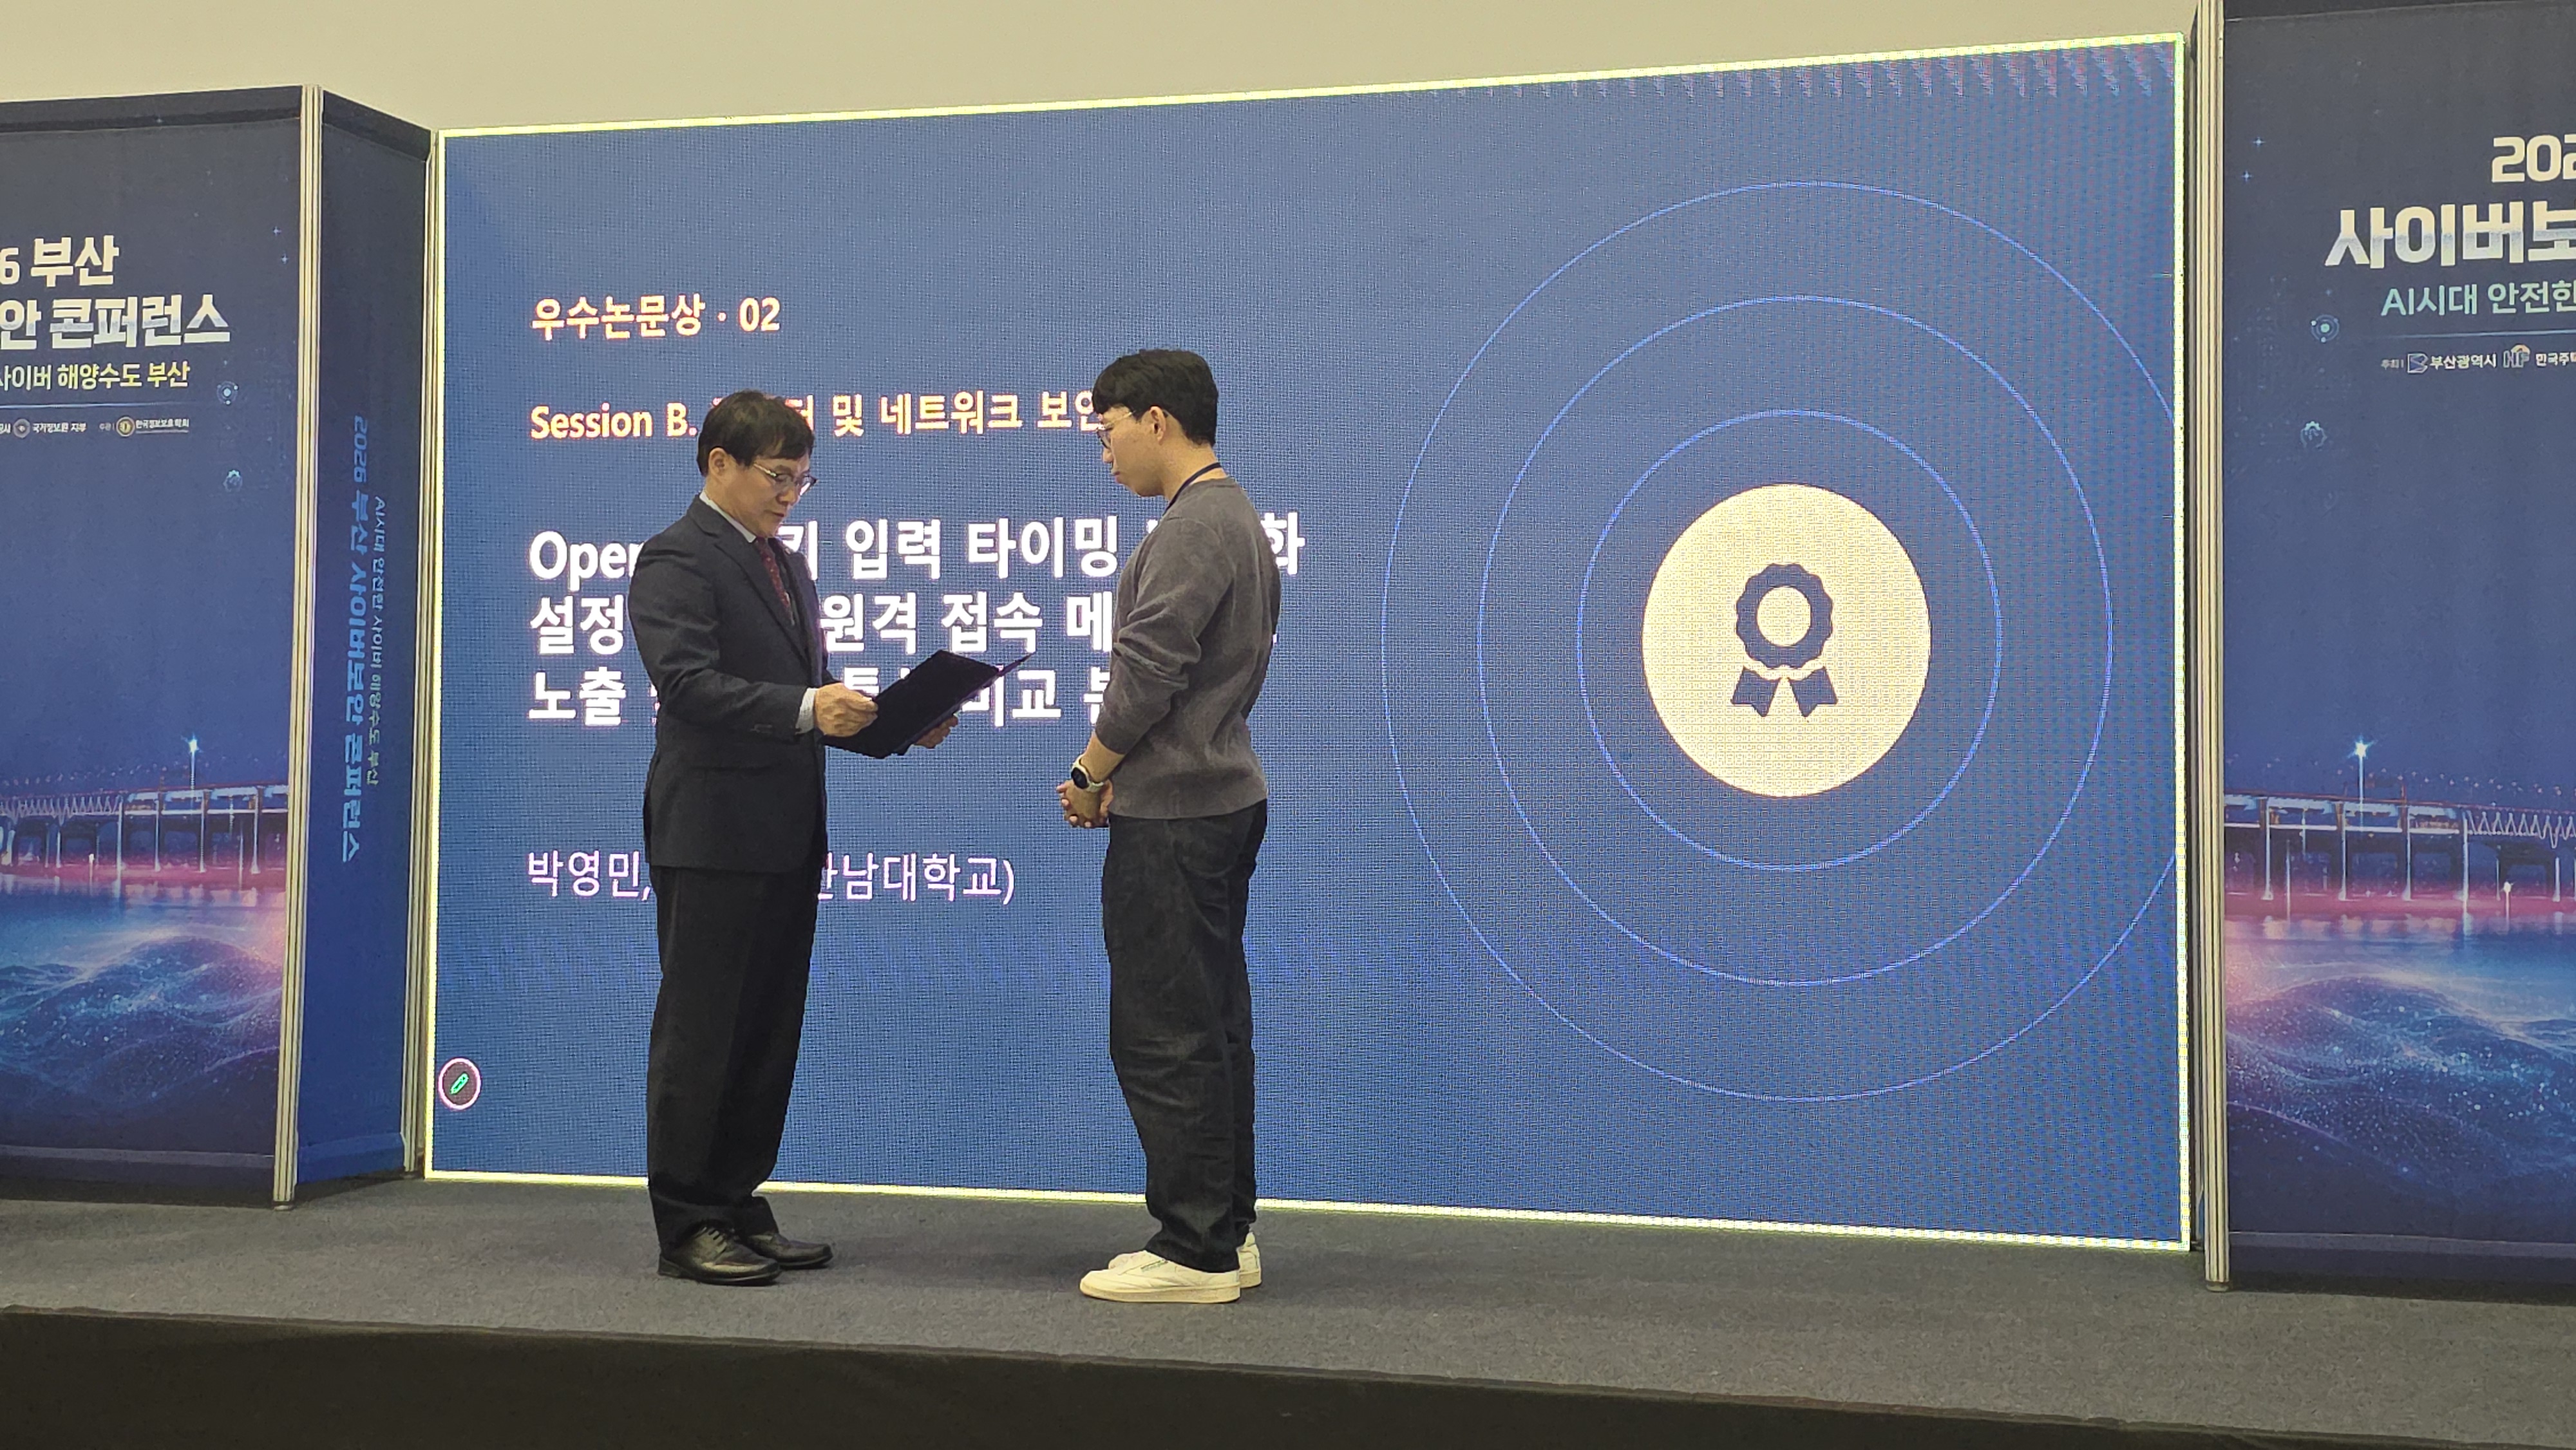 Award & Recognition
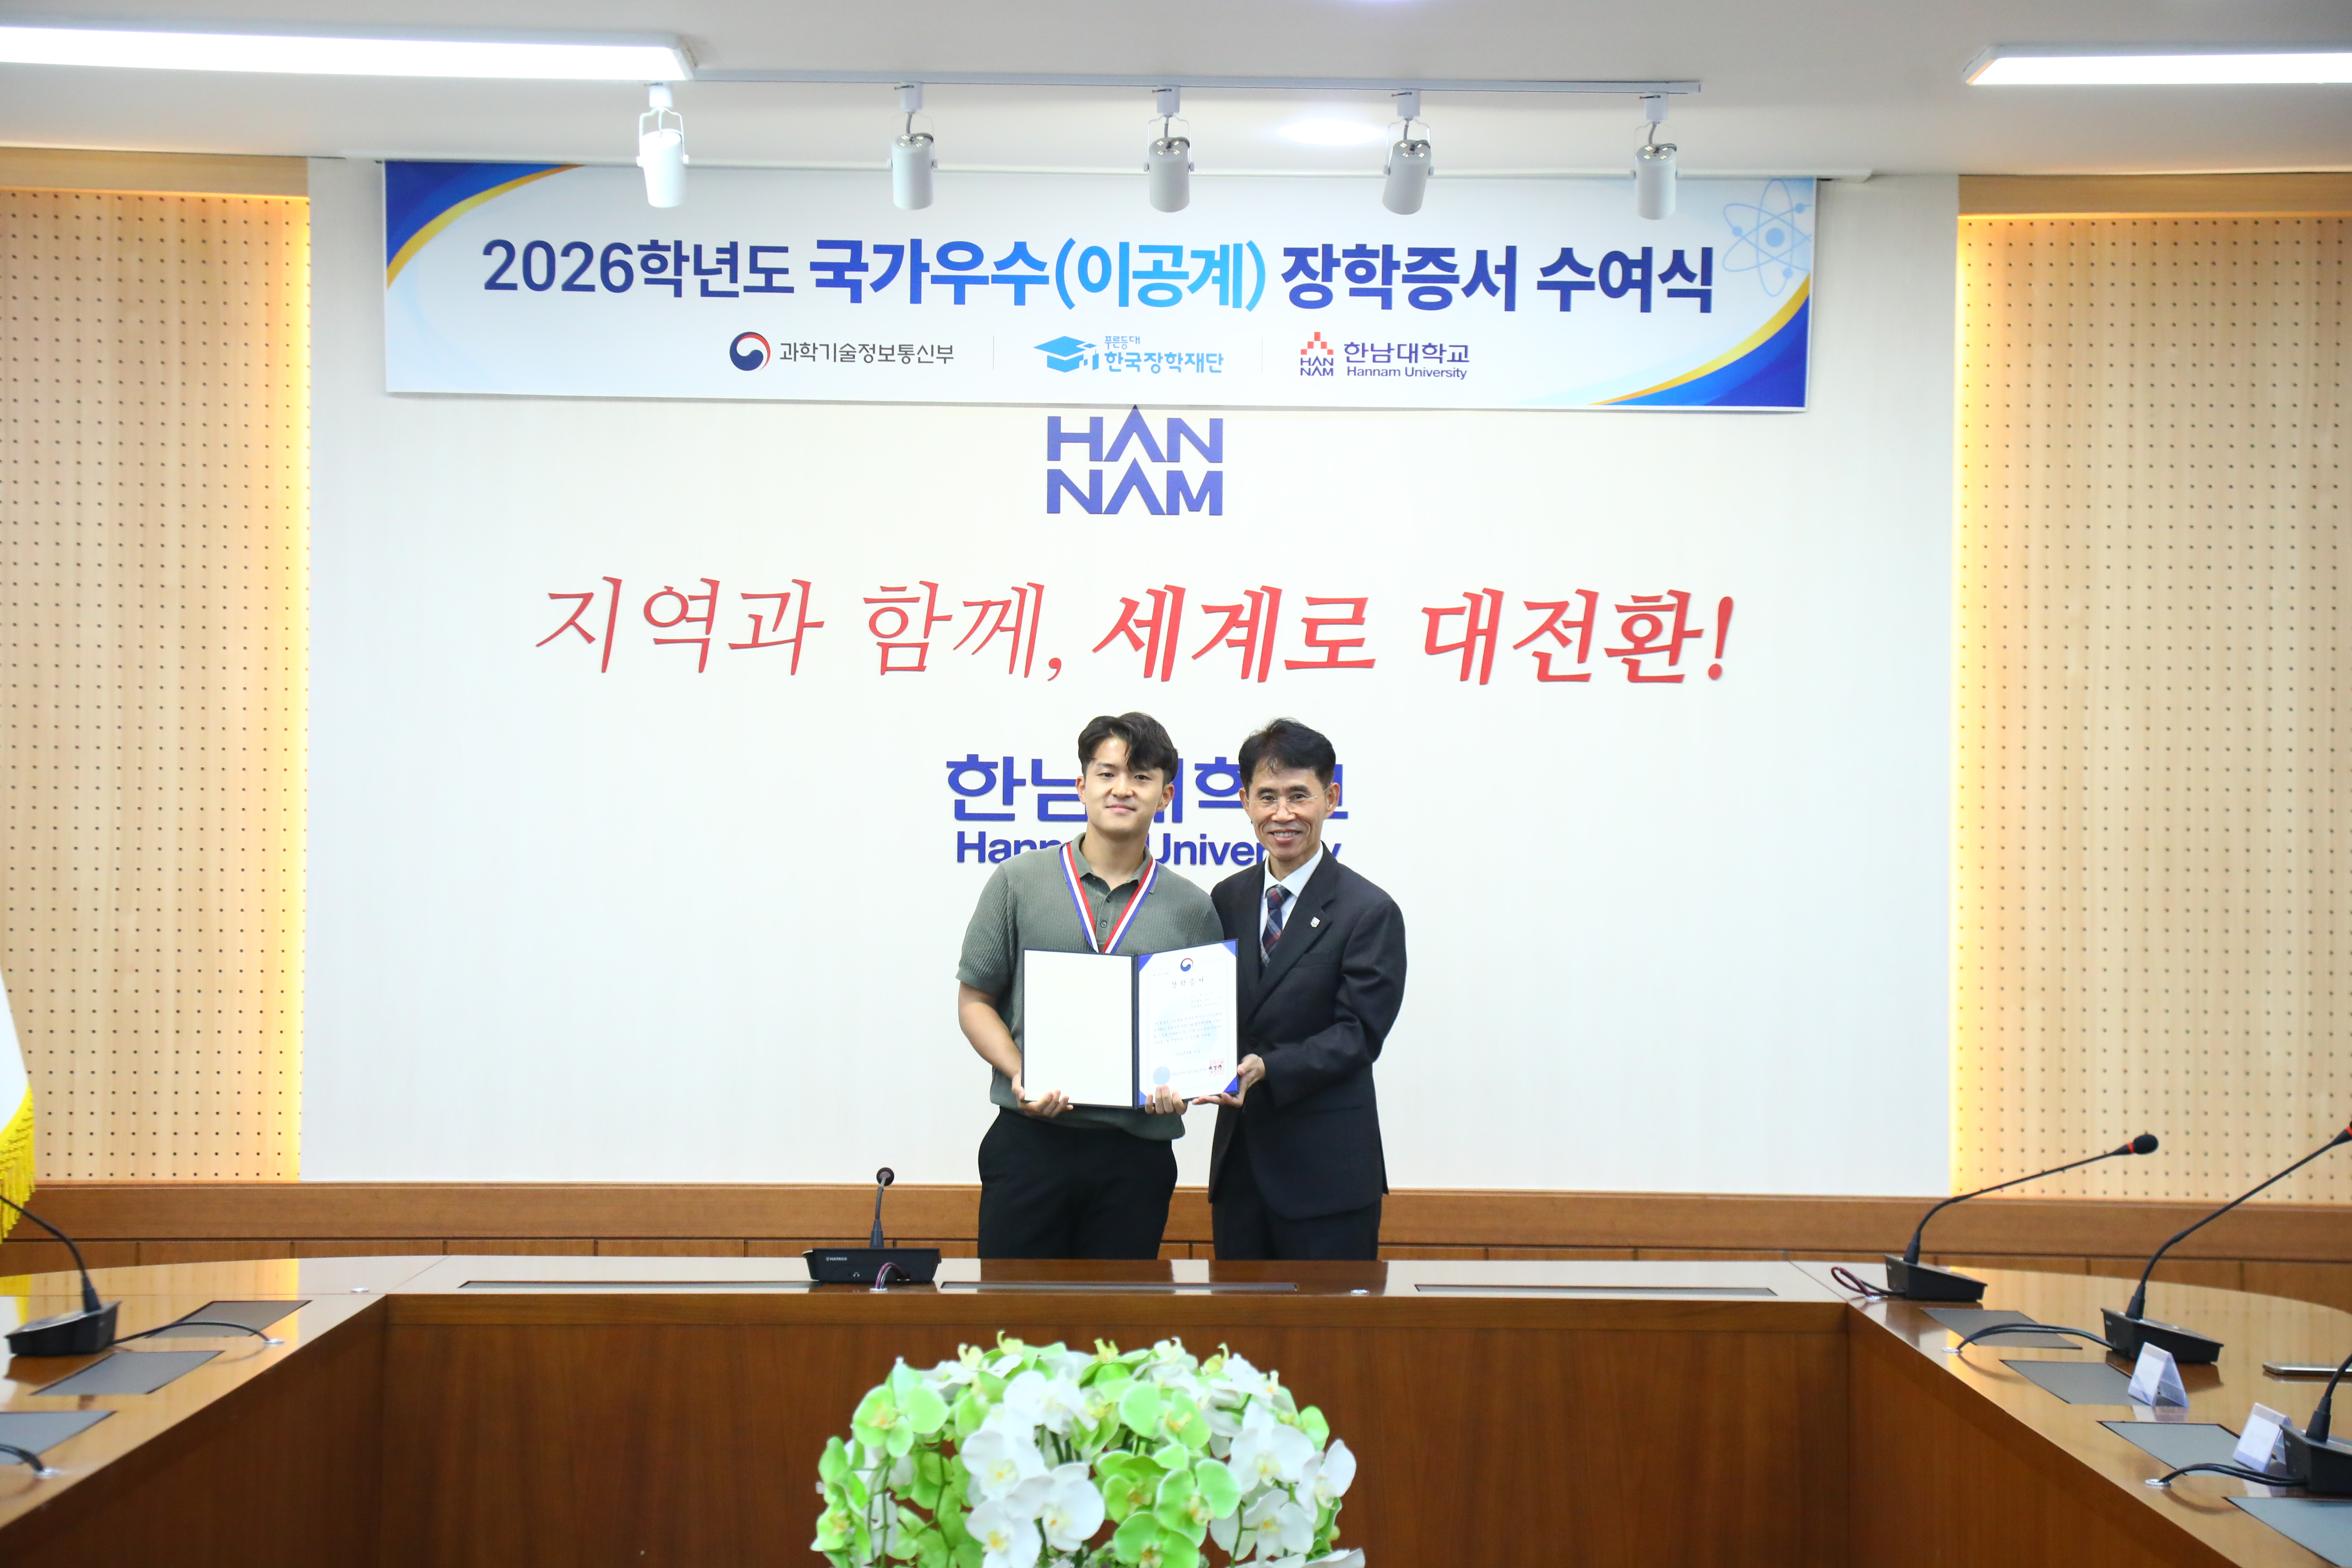 Award & Recognition
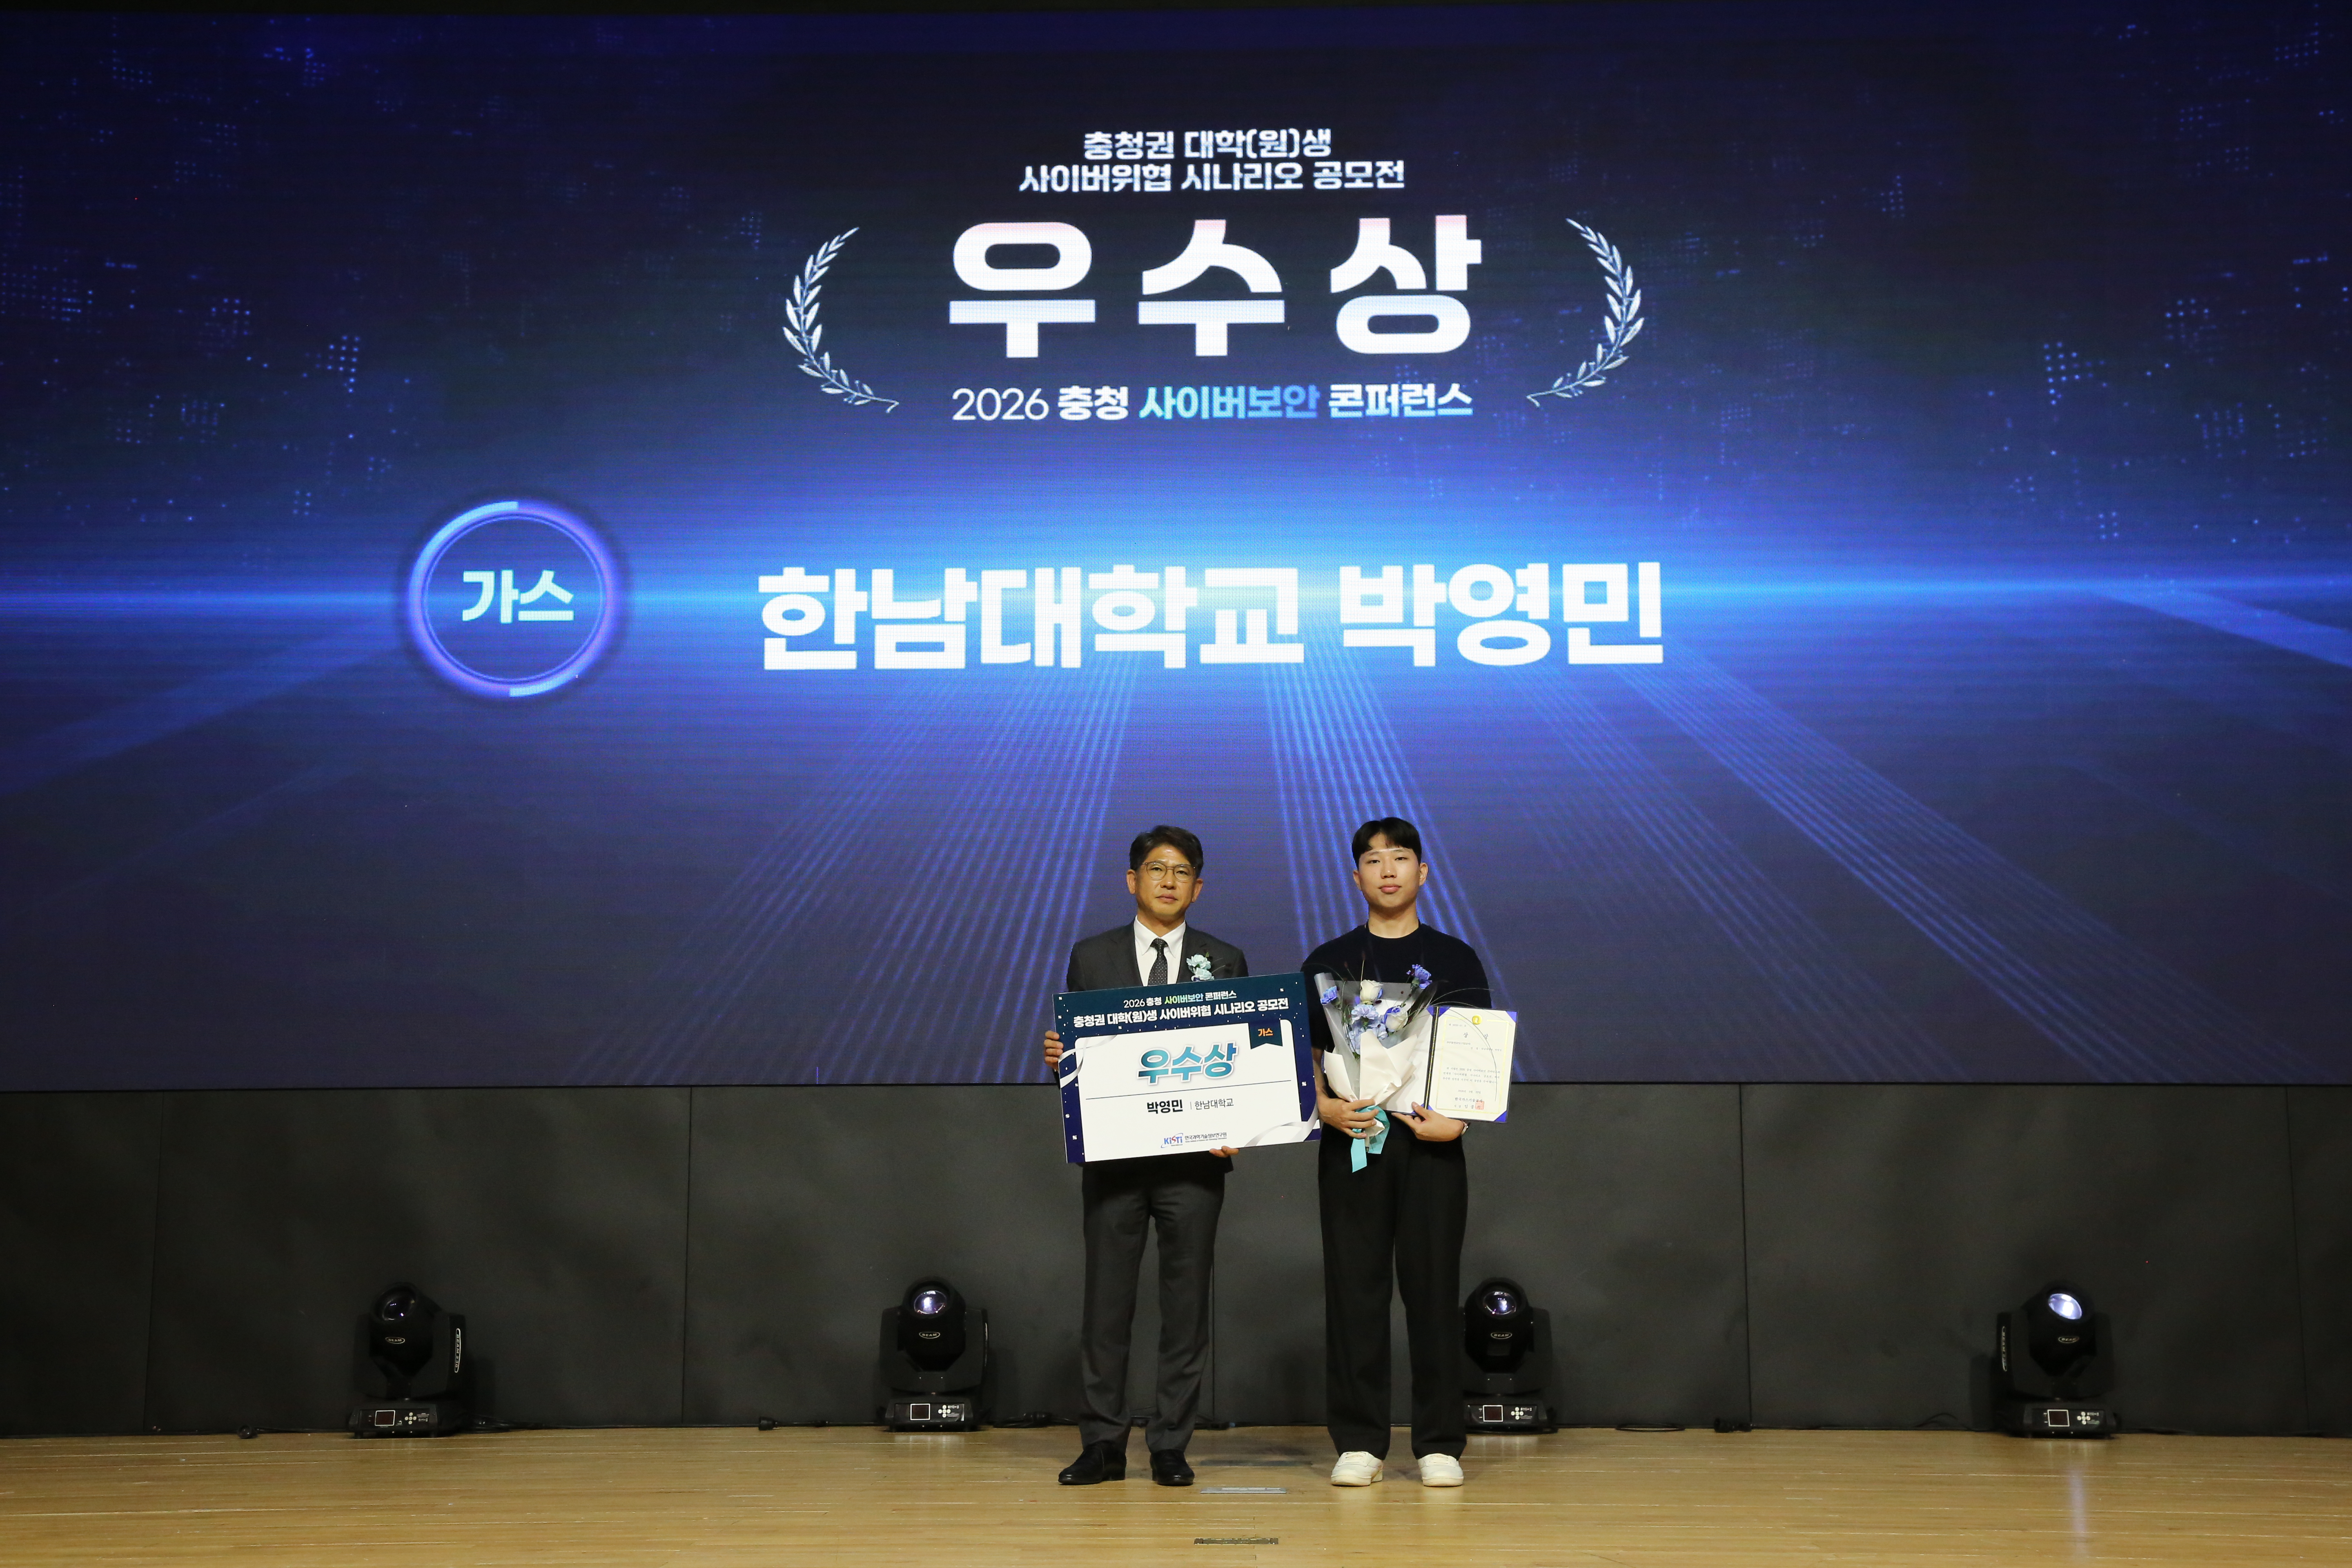 Award & Recognition
Join the conversation
We welcome inquiries regarding graduate admissions (M.S. & Ph.D.), industry-academia collaborations, technical consulting, and academic seminars.
lab.hpsc@gmail.com ↗College of Engineering, Hannam University
70 Hannam-ro, Daedeok-gu, Daejeon, Korea